For more than a decade, FastNetMon Community has given network operators an open-source option for high-performance DDoS detection.
Today, we’re extending that approach from detecting attacks to filtering them.
We are proud to announce FastACL Community, an open-source packet filtering engine for FD.io VPP, built to deliver DDoS filtering at exceptionally high packet rates and throughput.
Performance has been a core focus from the start. In our testing on a single AMD EPYC 7742-based platform, FastACL achieved 270 Mpps with 64-byte packets and full 400 Gbps throughput (2 × 200 GbE) with medium-sized packets.
FastACL runs inline, enforcing filtering rules to drop identified attack traffic while forwarding permitted traffic. Combined with FastNetMon—or another detection and orchestration system—FastACL provides the filtering data plane for building an open-source DDoS mitigation pipeline on commodity hardware.
We believe FastACL Community is the world’s first open-source DDoS scrubbing data plane built for commodity hardware.
From detection to scrubbing
FastNetMon Community already provides the detection side of the equation: analysing network traffic, identifying attacks in real time, and triggering external mitigation actions such as BGP announcements.
FastACL Community brings that same open-source approach to the mitigation data plane.
The concept is simple:
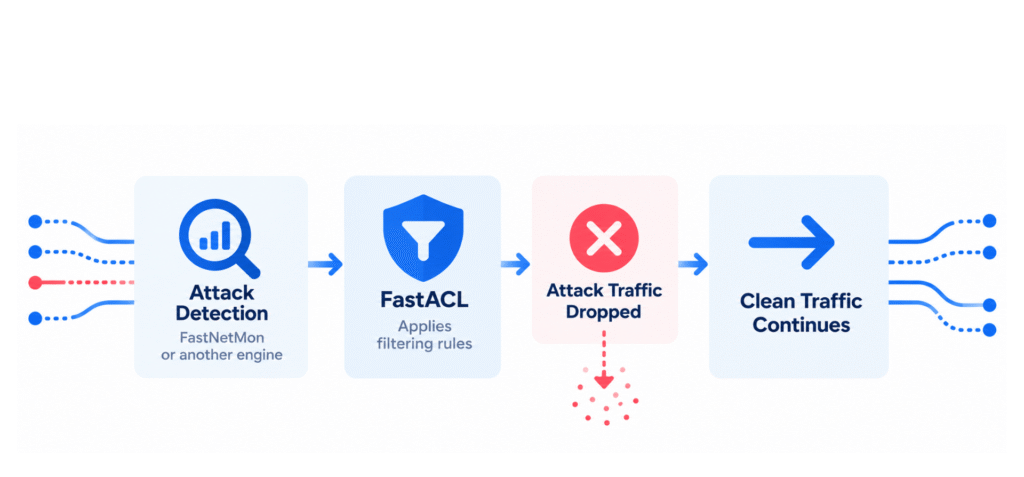
Under the hood, FastACL is implemented as a native FD.io VPP plugin and is designed for high-volume inline packet processing on commodity servers. Our development has focused on scaling both packet-processing performance and filtering capacity, from hundreds of millions of packets per second and hundreds of gigabits of traffic to configurations with up to one million active filtering rules.
FlowSpec-style filtering for IPv4 and IPv6
FastACL Community implements all 12 matching components defined by the RFC 8955/8956 BGP FlowSpec model, for both IPv4 and IPv6.
This includes filtering based on source and destination prefixes, protocols, ports and port ranges, ICMP fields, TCP flags, packet length, DSCP, and fragmentation flags.
It also provides permit and drop actions, per-rule and aggregate counters, packet sampling, and both CLI and binary API control.
In other words, FastACL provides the high-performance filtering engine while leaving operators in control of how attacks are detected and how mitigation policies are generated.
Building an open DDoS mitigation stack
For us, FastACL Community represents an important next step for the FastNetMon open-source ecosystem.
FastNetMon Community made it possible to build high-performance DDoS detection without relying entirely on proprietary systems. With FastACL Community, we’re bringing that philosophy to the system that actually processes and filters attack traffic.
FastACL Community is released under the Apache License 2.0 and is available now on GitHub.