by FastNetMon | Aug 13, 2025 | FastNetMon Blog
MadeYouReset is a new HTTP/2 DDoS vector related to 2023’s Rapid Reset. By provoking the server to reset streams with malformed frames, an attacker keeps backend request processing alive while freeing the stream from HTTP/2 accounting. One TCP connection can...
by FastNetMon | Aug 12, 2025 | FastNetMon Blog
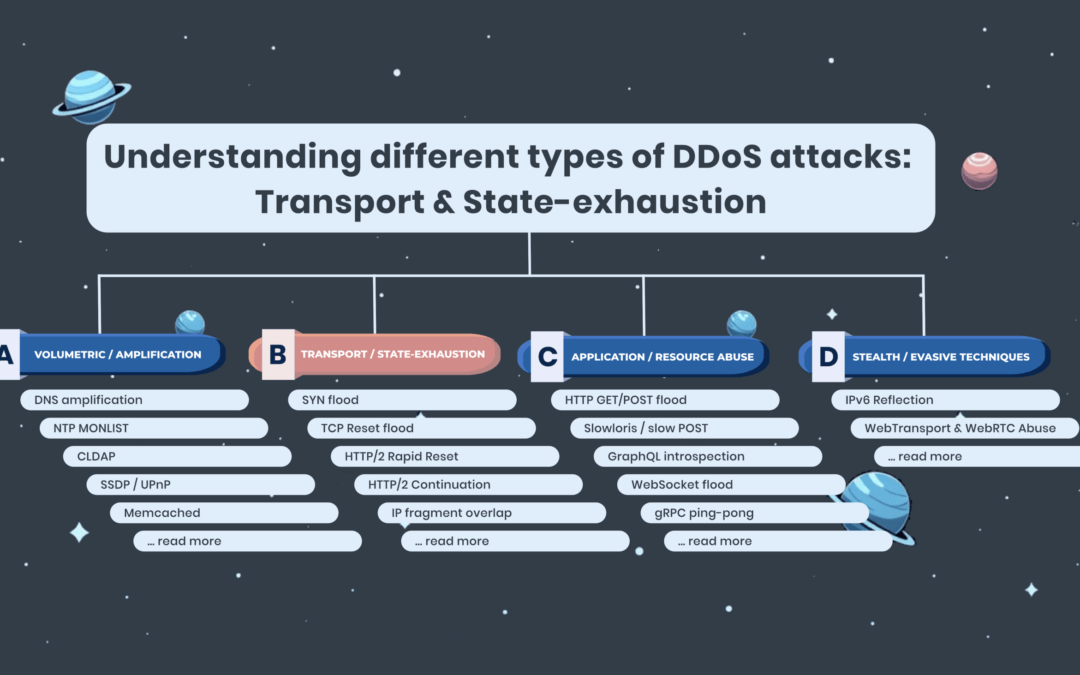
How connection state exhaustion attacks threaten your firewalls and proxies Transport and state-exhaustion DDoS attacks represent a growing and sophisticated category of denial-of-service threats targeting the resource limitations of network infrastructure. Instead of...
by FastNetMon | Aug 11, 2025 | FastNetMon Blog
SafeBreach Labs researchers Or Yair and Shahak Morag disclosed a new class of Windows denial-of-service (DoS) vulnerabilities that can be exploited to crash critical infrastructure or conscript publicly accessible Windows Domain Controllers (DCs) into high-bandwidth...

by FastNetMon | Aug 5, 2025 | FastNetMon Blog
If you’ve managed a network for more than a week, chances are you’ve seen it, or at least worried about it: the DDoS attack. You know the symptoms. Traffic spikes. Routing instability. Customers raising tickets before monitoring even kicks in. But how did we get here?...

by FastNetMon | Aug 5, 2025 | FastNetMon Blog
August 3, 2025, a crypto mining pool called Qubic claimed it was hit by a Distributed Denial-of-Service (DDoS) attack after launching an aggressive bid to gain control of the Monero blockchain. While no impact was observed on the Monero network itself, the events...


