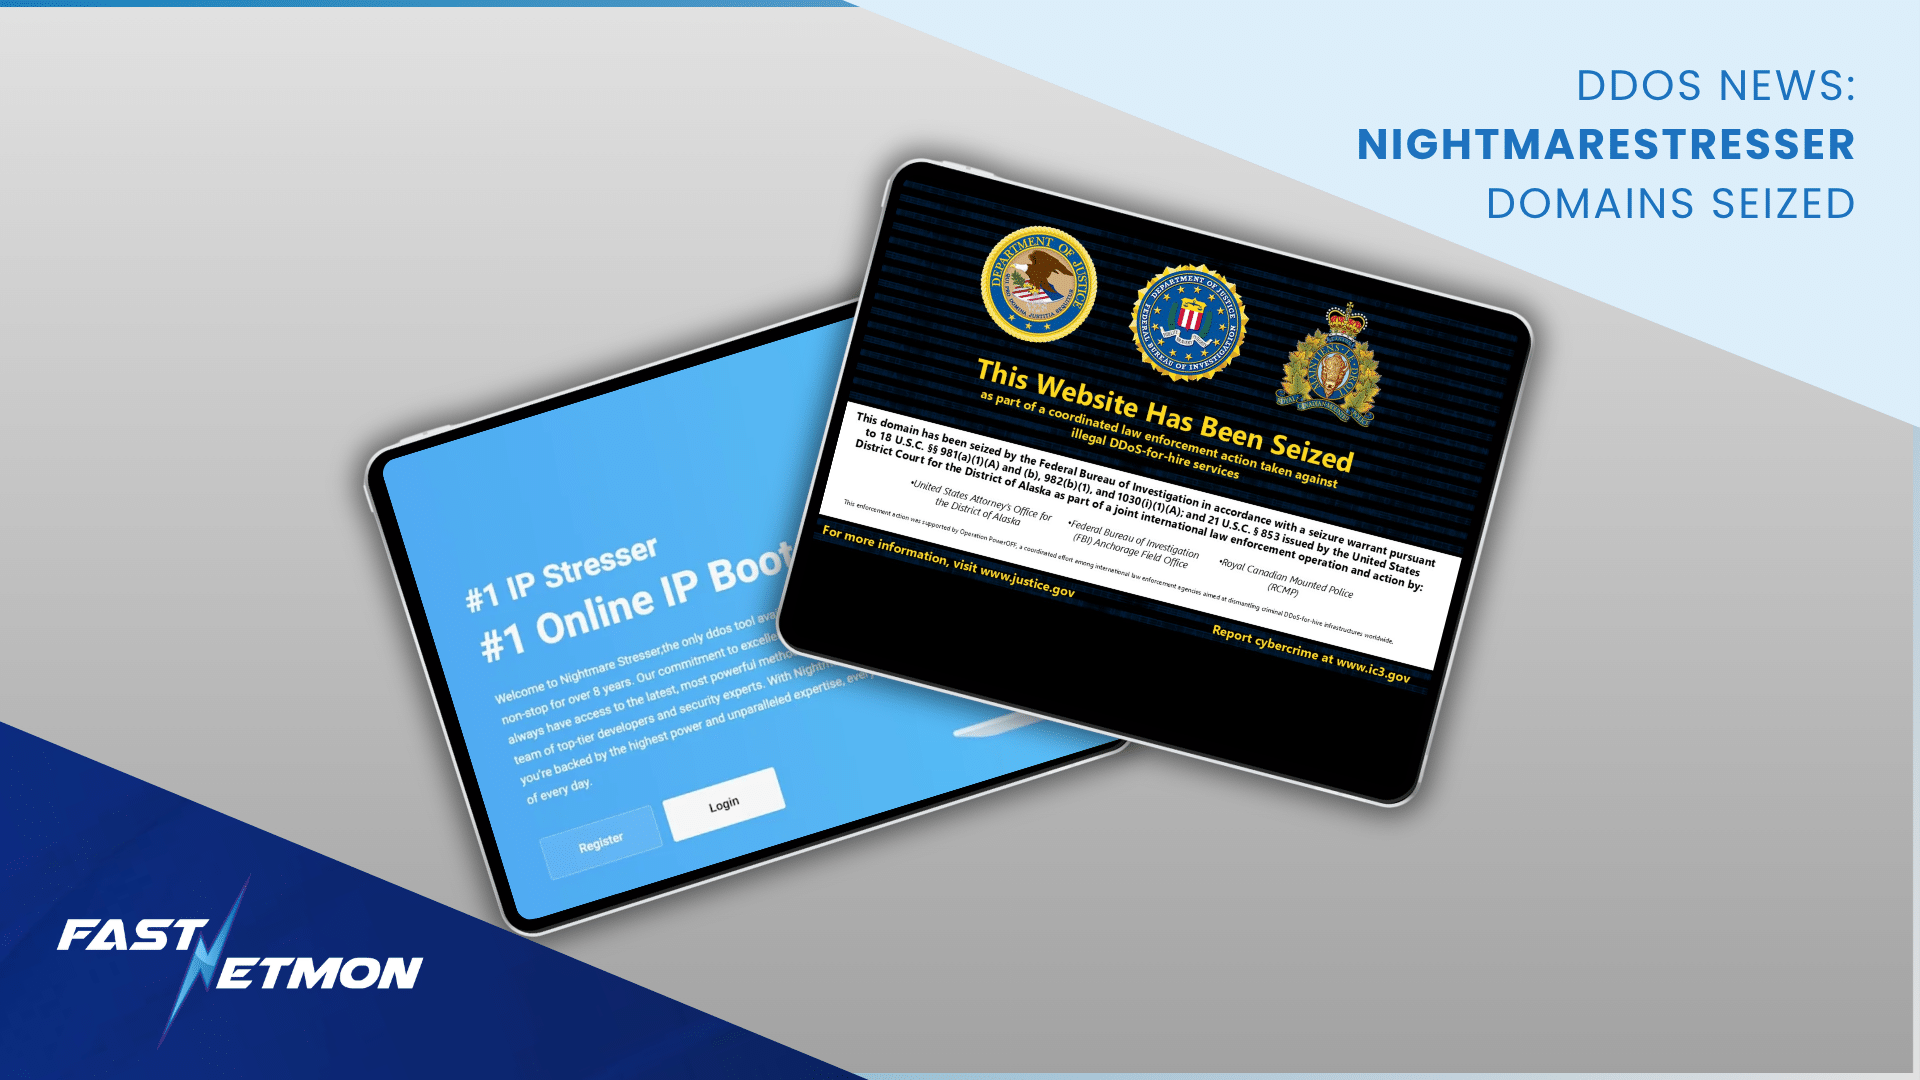
The FBI has seized internet domains associated with NightmareStresser, a long-running DDoS-for-hire service accused of enabling hundreds of thousands of actual or attempted attacks worldwide.
The action is part of Operation PowerOFF, an international law-enforcement effort targeting criminal DDoS-for-hire services.
According to the U.S. Department of Justice, NightmareStresser was used to launch hundreds of thousands of actual or attempted DDoS attacks against victims worldwide since 2022.
The seizure is another win in the effort to make commercial DDoS services harder to operate and access. However, the DOJ announcement specifically confirms the seizure of NightmareStresser's internet domains. It does not announce arrests or the seizure of the underlying attack infrastructure.
NightmareStresser disruption at a glance
- Service: NightmareStresser
- Type: DDoS-for-hire / booter / stresser
- Action: Internet domains seized
- Agencies: FBI and Royal Canadian Mounted Police
- Operation: Operation PowerOFF
- Reported activity: Hundreds of thousands of actual or attempted DDoS attacks since 2022
- Arrests announced: None
- Attack infrastructure seized: Not announced
What is NightmareStresser?
NightmareStresser is a DDoS-for-hire service, also known as a booter or stresser, that allowed customers to purchase access to DDoS attack capabilities.
Services like this lower the barrier to launching a DDoS attack. A customer does not need to build a botnet or operate attack infrastructure directly. Instead, the service provides an interface through which attacks can be purchased and launched.
The DOJ says booter services continue to proliferate because they provide a low barrier to entry for cybercriminal activity.
NightmareStresser appears to have operated at significant scale. Beyond the hundreds of thousands of actual or attempted attacks cited by the DOJ, some independent sources estimate that the service approached one million registered users by 2025 and was capable of generating thousands of attacks per hour.
Earlier independent research also cited more than 566,000 registered users and 52 dedicated servers in 2023.
These additional figures are estimates reported by third-party cybersecurity sources rather than numbers confirmed in the DOJ's latest announcement.
What did the FBI actually seize?
The DOJ announced the court-authorized seizure of internet domains associated with NightmareStresser.
Reporting identifies the affected domains as:
nightmare-stresser[.]comnightmarestresser[.]org
The domains now display FBI seizure notices.
Removing established domains disrupts access to a DDoS-for-hire service and forces its operators to rebuild the connection with their customers. It can also create additional costs, operational friction and investigative opportunities.
However, a domain seizure is not the same as dismantling the underlying DDoS infrastructure.
A simplified DDoS-for-hire service might look like this:
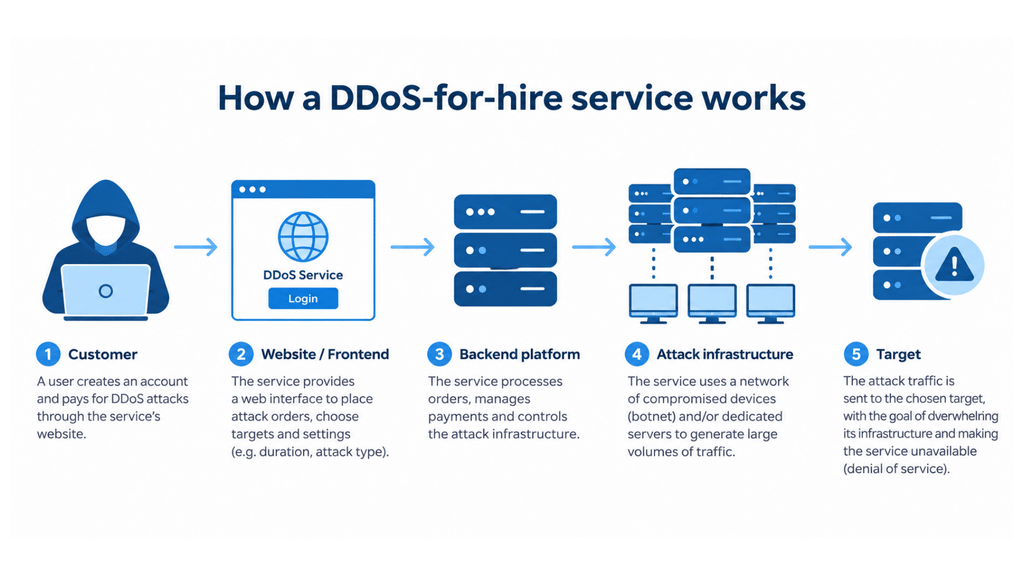
Seizing the domain disrupts an important part of that chain. The DOJ announcement does not state that NightmareStresser's backend servers, databases, payment infrastructure or systems used to generate attack traffic were seized.
No arrests were announced as part of this specific action.
What is Operation PowerOFF?
Operation PowerOFF is an ongoing international law-enforcement effort targeting DDoS-for-hire infrastructure, operators and users.
The NightmareStresser seizure was conducted by the FBI Anchorage Field Office in coordination with the Royal Canadian Mounted Police.
According to the DOJ, previous investigations involving prosecutors and investigators in Anchorage and Los Angeles over the past eight years have resulted in 12 defendants being charged for facilitating DDoS-for-hire services and the seizure of more than 100 associated domains.
This sustained pressure matters. Even when an individual action does not eliminate all of a service's infrastructure, repeated domain seizures, investigations, infrastructure disruption and arrests make DDoS-for-hire platforms more difficult and risky to operate.
Could NightmareStresser return?
It is too early to know whether NightmareStresser will permanently disappear.
If its operators retain the underlying infrastructure, they could potentially attempt to move the service to new domains. Independent reporting indicates that a domain associated with NightmareStresser was included in an earlier U.S. enforcement action in 2022, after which the service continued operating.
But rebuilding isn't without cost. Operators need to establish new domains and communication channels, reconnect with customers and potentially expose additional infrastructure in the process.
The latest action should therefore be viewed as part of a broader strategy of increasing the cost, friction and risk of operating DDoS-for-hire services.